ADFS
Prerequisites
- A Windows Server that:
- Has ADFS configured.
- Has the latest Visual C++ Redistributable.
- Has the SecurEnvoy Microsoft Server Agent.
- A Windows machine with the Single Agent.
1. SecurEnvoy RADIUS Profile
- Go to Integration > Premises and add a new RADIUS profile.
- Enter the RADIUS configuration settings:
- Friendly Name.
- Server Port.
- Assigned Agent.
- The IP address of the ADFS server.
- The Shared Secret for the RADIUS connection.
- (Optional) Enable the 'Message Authenticator' and 'Brute Force Protection' options.
- Save the configuration.
2. Microsoft Server Agent Installation
- Go to the Microsoft Server Agent Config utility
- Enter the RADIUS configuration settings:
- The IP address of the Single Agent
- The Shared Secret for the RADIUS connection
- The RADIUS Port
- Click 'Update' to save the configuration.
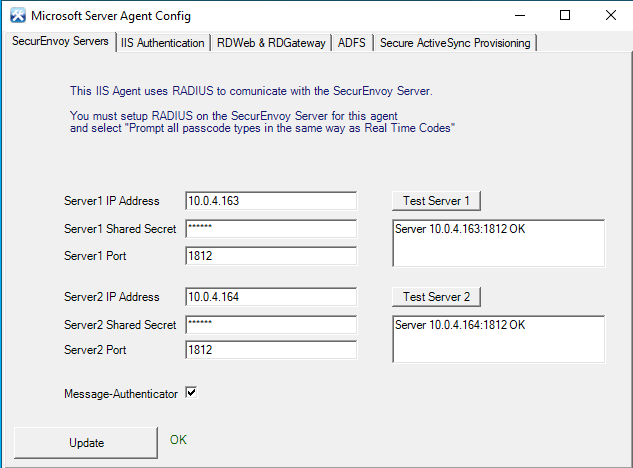
Multiple Single Agents
Up to two Single Agents can be added in the Microsoft Server Agent. Each agent will require a RADIUS profile in Access Management.
3. Microsoft Server Agent config
- Go to the 'ADFS' tab and click the checkbox for 'Include SecurEnvoy Plugin in ADFS'
- Click 'Update' then 'Start ADFS Manager'
4. ADFS Config
- In ADFS Manager go to: Action > Add Relaying Party Trust.
- Select 'Claims Aware' and click 'Start'.
- Enter your Federation metadata and click 'Next'.
- Select 'Permit everyone and require MFA' then click 'Next'.
- Check the settings and finish the wizard.
- Expand 'Service' and click 'Authentication Methods' then click 'Edit Primary Authentication Methods'.
- On the 'Additional' tab, check 'SecurEnvoy'.
5. Testing MFA Authentication
- Open a browser and go to the ADFS URL to log in as a user.